Start with the access boundary, not the provider label
Treat the first external commitment as a gate on uncertainty and access, not as a choice between provider labels. Before a fund asks an outside party to enter its systems or take on broader responsibility, record four things: the unresolved decision, the information and systems involved, the internal decision owner, and the output that will be reviewed.
Use this commitment record:
- Unresolved decision: What must the fund decide about architecture, integration, modernization, implementation, or controls?
- Information boundary: What information is collected, processed, or stored, where it resides, and which systems use it?
- Decision rights: Which choices remain with the fund, and who approves access, scope changes, and acceptance?
- Reviewable output: What requirements, options, assessment, implementation, documentation, or support activity will exist for review?
The record determines the next commitment. When technical direction remains unsettled, ask for a bounded analysis of requirements, options, or risks. When the direction and development plan are clear but internal capacity is limited, consider additional engineering capacity. When the outcome, responsibilities, and acceptance conditions are defined, a project proposal can be evaluated. When the information boundary is unclear, keep the work at assessment until the fund can describe what access is needed and why.
This is a decision sequence rather than a permanent classification. A fund may move from analysis to implementation, or from a defined project to added capacity, but each move should have a stated reason, a new access decision, and a review point. U.S. technology consulting commonly uses project-based, retainer, and staff-augmentation structures; the structure affects contract terms, risks, and deliverables, but it does not answer the fund’s unresolved question by itself.
The first gate is passed when the fund can state the question, the permitted information boundary, the accountable internal owner, and the output that will support the next decision. If one of those items is missing, narrow the request rather than asking for a broad commitment.
Assign authority to artifacts and decisions
A software development consultant is useful when the fund needs an external party to connect a technology need with an examined approach, an implementation activity, or a managed technical task. The role should be bounded by decisions and artifacts rather than by a general promise of expertise.
The supplied role description supports activities such as:
- analyzing requirements and organizational needs;
- identifying technical strategies;
- developing or implementing software solutions;
- documenting requirements and specifications;
- managing projects or development activities;
- providing technical support; and
- training users of a new system.
Turn those activities into an authority map before work begins. For each requested activity, record the question being addressed, the artifact or action expected, the person who reviews it, and the decision that remains with the fund. For example, a requirements assessment can produce documented requirements; an architecture review can produce options and trade-offs; implementation can produce an agreed component; and support can produce a defined response activity. The agreement should state which of these is included.
This map also prevents responsibility from expanding by implication. A consultant may analyze requirements without owning the fund’s investment process. A provider may review a technology environment without determining whether the fund satisfies every applicable legal or regulatory obligation. The fund should identify who approves access, accepts technical work, handles incidents, administers permissions, and decides what happens after handoff.
Ask the provider to connect each proposed activity to four points:
- What information or system context is needed?
- What work will be performed or produced?
- What decision can the resulting output support?
- Which responsibility remains with the fund?
A scope that names only “technical expertise” leaves the commitment gate open. A scope that names an examined requirement, documented option, implemented component, support activity, or training task gives the fund something to review and a clear boundary for the next access decision.
Make the first commitment reversible
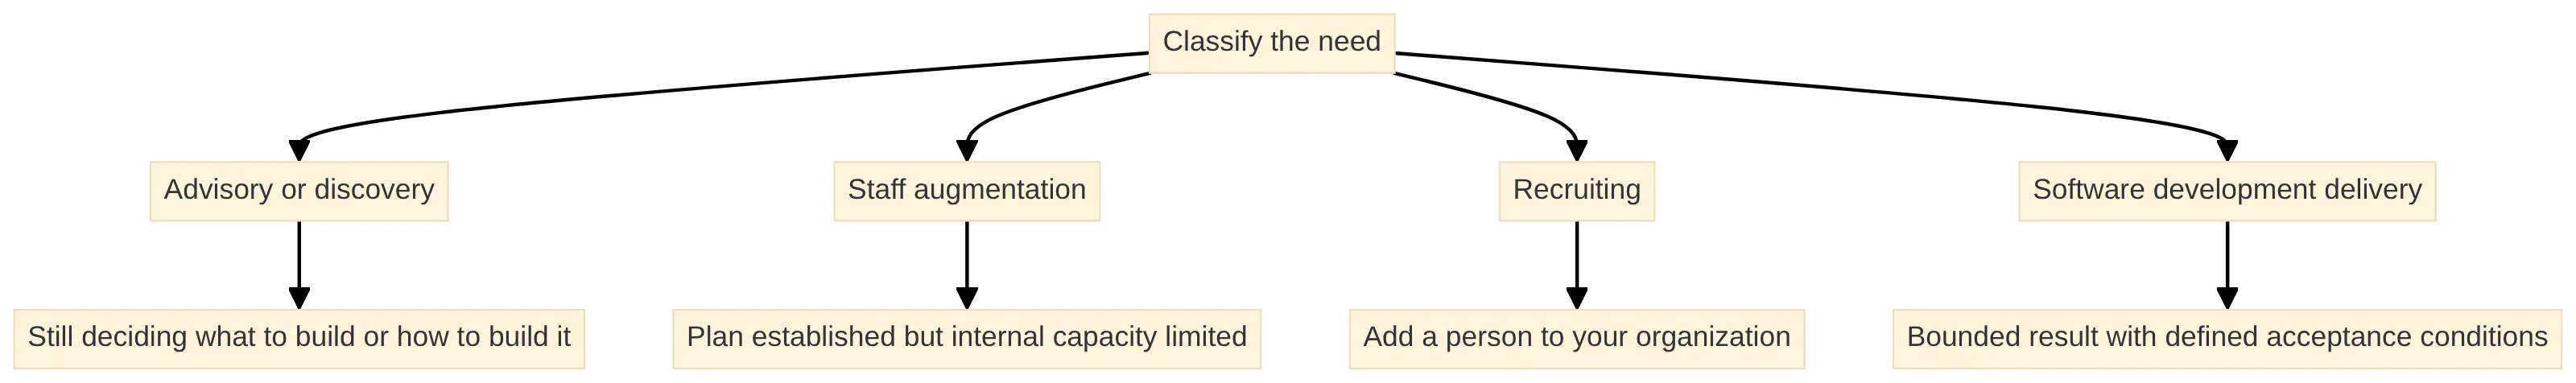
Choose the first commitment by asking how much uncertainty the fund is willing to carry forward and how easily the work can be narrowed if the answer changes. Advisory work, staff augmentation, recruiting, and software delivery are not interchangeable ways to obtain software help.
Advisory or discovery work is the narrower starting point when important choices remain unresolved. Its possible outputs include analyzed requirements, technical options, documented specifications, risk questions, or a plan for a later phase. The fund should define the question to be examined and the decision that the output will inform.
Staff augmentation addresses additional engineering capacity when the development plan is already clear. The fund must state who directs priorities, reviews work, approves access, and makes technical decisions. Adding engineers does not by itself settle an unresolved architecture or information boundary.
Recruiting addresses adding a person or candidate to the fund’s own organization. It follows a different decision path from engaging an external party to assess a system, implement a component, or provide technical support.
Software development delivery addresses an agreed implementation outcome. The scope should state the component or result, responsibilities, acceptance conditions, dependencies, and handoff. A delivery proposal is difficult to compare when the fund is still deciding what should be built or which constraints apply.
Use an exit condition for the first phase. An advisory phase can end with a documented decision and a recommendation about whether to proceed. A capacity phase can end when the agreed work or period is complete. A delivery phase can end at acceptance and handoff. A recruiting process can end with a hiring decision. These endpoints make it possible to narrow or stop the commitment without treating every engagement as a route to a larger one.
A staged path can combine these forms, but each stage should retain its own purpose and decision rights. The useful question is not which label sounds broader. It is whether the proposed first step produces the information or work needed for the next gate without granting more access or responsibility than the current decision justifies.
Run the four-part commitment gate
Use a four-part commitment gate to decide whether an external engagement should remain narrow or move toward implementation, broader access, or continuing responsibility. The gate is a record of questions and evidence, not a ranking of providers.
1. Direction. State whether the fund is asking for expert input before committing to an approach or is executing a development plan that has already been established. If the direction is unsettled, define the analysis or discovery output first. If the plan is clear, state the engineering work that remains and the internal decisions that govern it.
2. Information. Describe the nature, sensitivity, and location of information the fund collects, processes, or stores, together with the systems that use it. SEC staff guidance says funds and advisers may wish, where relevant, to periodically assess these matters. Use that assessment to define the minimum information and environment access needed for the proposed work.
3. Controls. Identify the regulatory obligations, cybersecurity questions, technical constraints, review responsibilities, and operating dependencies relevant to the scope. A cybersecurity engagement may include assessment of security architecture, identification of gaps, risk assessment, policy and procedure review, and work on controls suited to the organization’s environment and risk profile. Those activities should not be expressed as a promise of a particular compliance or security result.
4. Accountability. Name the people who approve access, set priorities, make technical decisions, review work, accept outputs, and handle handoff. Record the provider’s responsibilities separately from the fund’s responsibilities. If a proposal describes tasks but not decision rights or acceptance conditions, the gate is incomplete.
For supplier diligence, request information that helps define the boundary: traceable company information, relevant supply-chain tiers, foreign influence or ownership, provenance, resilience, and foundational cyber practices. These questions help the fund determine what must be examined before a supplier receives broader access; they do not replace the fund’s own review.
Apply the gate in sequence. First, write the unresolved question. Next, define the least access and smallest output that could answer it. Then request evidence tied to that question. Finally, decide whether the result supports a broader scope, a different engagement structure, a narrower phase, or no further commitment.
For an undocumented or poorly understood system, do not use added capacity as a substitute for understanding the system. For a defined project, do not leave acceptance or handoff implicit. For a retainer, state its purpose, decision set, review cadence, response expectation, and limits. For augmentation, state team interfaces, repository and environment access, review responsibilities, and decision rights.
A project-quote inquiry is ready when the fund can state its business objective, systems context, constraints, required expertise, responsibilities, and evaluation criteria. If the direction or information boundary remains open, ask for the bounded work that will answer those questions instead of requesting a fixed delivery commitment. Expand only when the next responsibility, access request, evidence review, and acceptance path are recorded.
Sequence discovery before augmentation when systems are undocumented
An undocumented legacy system creates a knowledge problem before it creates a staffing problem. If you add engineers before the system, dependencies, and migration constraints are understood, you may increase activity without resolving the uncertainty that governs the work.
Discovery consulting followed by augmentation is a suitable pattern for an undocumented legacy system that must be migrated. The sequence matters because discovery can establish what the system does, where information moves, which dependencies exist, and what decisions must precede implementation.
Treat the discovery phase as a bounded investigation. Ask for outputs such as:
- a description of the system boundary and major dependencies;
- a record of known interfaces, data movements, and operational assumptions;
- documented requirements for the intended migration or modernization;
- a list of unresolved technical and ownership decisions;
- options with stated trade-offs; and
- a proposed implementation boundary for any later engineering phase.
These outputs do not prove that a migration will succeed or that every dependency has been found. They give you material to examine before expanding access, scope, or team size. The acceptance test should therefore focus on whether the agreed questions were investigated and whether the resulting decisions are documented, not on a promise of a particular migration outcome.
Ask the provider to separate known facts, working assumptions, open questions, and recommendations. Request an explanation of how the provider will work with people who understand the existing system and how knowledge will be transferred into your organization. Identify who approves a migration decision and who owns the resulting system.
Move to augmentation only after the discovery output supports a sufficiently clear plan. If major system boundaries, dependencies, or ownership questions remain unresolved, keep the next phase narrow and investigative. If the plan is clear and capacity is the primary gap, an augmentation structure becomes easier to assess against defined work.
Set the financial-services control boundary before modernization
Define the engagement’s access boundary before modernization work reaches sensitive information or important operating systems.
Start with the information and systems involved. Record whether the proposed work touches portfolio information, client information, internal research, credentials, production services, development environments, or third-party platforms. Then identify what access is necessary for the stated task and what access is unnecessary. The boundary should cover people, environments, repositories, interfaces, data, credentials, and the period for which access is granted.
SEC staff cybersecurity guidance says funds and advisers may wish, where relevant, to periodically assess the nature, sensitivity, and location of information they collect, process, or store, together with the technology systems they use. The guidance presents this as a measure to consider, not as a conclusion about your fund’s individual obligations.
Use that principle to make the provider discussion concrete:
- Which information categories will the work require?
- Where are those categories stored and processed?
- Which environments may the provider access?
- What controls already apply to those environments?
- Who authorizes access, reviews activity, and ends access?
- Which responsibilities remain with your fund’s security, technology, and compliance teams?
Modernization should also have an operational boundary. Define whether the provider is advising, coding, testing, deploying, monitoring, or supporting a system. Do not treat a proposal to improve software as permission to change production controls or operational responsibilities.
A provider can contribute technical work within a defined boundary, but your fund remains responsible for deciding how the engagement fits its governance and obligations. Put that decision before the commercial commitment, and make the conditions visible in the inquiry and proposed statement of work.
Evaluate security work through observable evidence
Security capability should be evaluated through observable work, defined responsibilities, and relevant evidence rather than through a broad assurance statement. A cybersecurity consultant may assess existing security architecture, identify gaps, evaluate risks, review policies and procedures, and help establish controls suited to the organization’s technology environment and risk profile.
Translate those activities into questions about the proposed engagement:
- What architecture or environment will be assessed?
- Which risks and gaps are within scope?
- What method will the provider use to record findings and prioritize them?
- Which policies or procedures will be reviewed?
- What control recommendations will be produced?
- Who decides whether a recommendation is accepted, deferred, or rejected?
- What evidence will show that an agreed action was completed?
Ask for anonymized examples of deliverables where permitted, such as an assessment structure, findings format, risk register, control-mapping approach, or remediation plan. The request is not for confidential client information. It is a way to see whether the provider can make its work inspectable.
These categories are evaluation prompts, not proof that a provider satisfies your requirements.
Separate security assessment from security ownership. An assessment can identify a gap; it does not by itself close the gap. A control recommendation can inform a decision; it does not establish that your fund has met every applicable obligation. Your scope should state who implements changes, who tests them, who approves residual risk, and who maintains the control afterward.
Use a decision gate before access expands: proceed only when the provider can explain the work, the evidence it will produce, the information it needs, and the responsibilities that remain with your organization. If those answers are vague, keep the engagement at a narrower assessment boundary.
Examine the information and supplier boundary
The information and supplier boundary includes more than the provider’s technical skills. It includes the organization you would contract with, the people and systems involved, the origin and handling of information, and the conditions under which the relationship can continue.
Use those categories to structure your inquiry:
- Traceability: Can you identify the contracting entity, operating locations, relevant contacts, and responsibilities?
- Supply-chain tier: Is the provider direct, or will subcontractors or other suppliers touch the work, information, or environment?
- Ownership and influence: What organizational relationships could affect control, access, or continuity?
- Provenance: Where do the provider’s services, tools, personnel, and relevant components originate?
- Resilience: How would the provider sustain the agreed work if staffing, systems, or operating conditions changed?
- Foundational cyber practices: What practices apply to the provider’s public-facing technology and development activity?
The questions should be proportionate to the work. A provider with no access to sensitive systems presents a different information boundary from a provider implementing code in a production-adjacent environment. State the difference rather than applying one undifferentiated checklist.
That gives you a reason to revisit the boundary when scope changes, not only when the relationship begins.
Request evidence that can be examined and retained: organizational details, relevant supplier disclosures, access responsibilities, subcontractor information where applicable, continuity arrangements, and descriptions of security practices. Do not treat a completed questionnaire as a substitute for deciding whether the proposed access and responsibilities fit your fund. Use the evidence to define the contract, the access model, and the review points.
Turn each open risk into an evidence request
Turn each open risk into an evidence request that can be reviewed at the commitment gate. A provider’s presentation is not a substitute for a record showing what the proposed team can examine, produce, access, and hand over.
Create an evidence register with one row for each material question. Record the question, the requested evidence, the person who will review it, the decision it informs, and the condition that remains open if the response is incomplete.
Use these evidence categories:
- Technical work: Ask how the proposed team analyzes requirements, documents specifications, develops or implements solutions, and handles support or handoff. Request an anonymized artifact or a walkthrough tied to the proposed type of work where appropriate.
- Financial-services context: Ask the team to explain how it would account for the operating realities, control expectations, and dependencies relevant to a financial organization.
- Information and access: Ask what environments, repositories, interfaces, and information categories are required, for what purpose, and for how long.
- Delivery responsibility: Ask how requirements, design decisions, review points, acceptance, changes, documentation, and handoff would be recorded.
- Communication and integration: Ask who communicates findings, who works with internal decision owners, and how unresolved questions are surfaced.
- Engagement boundaries: Ask why the proposed structure matches the current decision and what would cause the provider to narrow, pause, or change the scope.
For each response, distinguish among an answer about the proposed work, a relevant example or anonymized artifact, a named responsibility in the team and agreement, and a stated limitation. These are different forms of evidence. A response should not be treated as proof of a capability that it does not address.
The register should remain live after selection. When the proposed scope changes, add the new question before approving broader access or responsibility. When an item cannot be answered, make that limitation visible in the proposal or keep the work at the narrower gate. This turns evaluation into a sequence of decisions rather than a general impression of fit.
Record how responsibility changes when access expands
Record how responsibility changes when the fund moves from a bounded question to a larger commitment. U.S. technology consulting commonly uses project-based, retainer, and staff-augmentation structures, and each affects contract terms, risks, and deliverables. The useful comparison is how each structure assigns decisions, access, review, and handoff.
| Structure | Record before approval | Primary boundary |
|---|---|---|
| Project-based | The outcome, deliverables, acceptance conditions, change process, dependencies, and handoff | Do not treat an unsettled technical direction as a fixed delivery scope. |
| Retainer | The recurring purpose, decision set, review cadence, response expectation, and limit on work | Do not allow continuing access without a stated reason and review point. |
| Staff augmentation | The internal direction of work, team interfaces, repository and environment access, review responsibilities, and technical decision rights | Do not use additional capacity to conceal unresolved questions. |
Use the same responsibility chain for every structure: who defines the work, who performs it, who reviews it, who accepts it, who operates the result, and who decides on a change after handoff. Write those answers into the proposed scope rather than inferring them from the label.
The structure can change as the evidence changes. A fund may begin with a bounded analysis, then request a project proposal if the outcome becomes clear. It may instead request additional capacity when the plan is settled but execution resources are limited. A continuing advisory arrangement requires its own purpose and review cadence. Each transition should reopen the access boundary and identify the new decision owner.
Compare proposals by the responsibility record, not by the apparent flexibility of the model. A workable proposal shows what the fund controls, what the provider performs, what evidence will be reviewed, and what ends the current commitment.
Escalate evidence in proportion to requested access
Escalate evidence in proportion to the access and responsibility the fund is considering. The first request should test whether the proposed work fits the unresolved question. A later request should examine the people, systems, supplier boundary, and operating conditions involved before the commitment expands.
Use four checkpoints:
Checkpoint 1: written scope. Request the proposed objective, assumptions, activities, outputs, dependencies, responsibilities, access needs, review points, acceptance conditions, and circumstances that would narrow or pause the work.
Checkpoint 2: technical explanation. Ask the people proposed for the work to explain how they would analyze requirements, document specifications, develop or implement the relevant solution, manage the activity, or support the result. Request an anonymized example or decision record where it helps the fund assess the proposed work.
Checkpoint 3: access and supplier boundary. Ask which environments, repositories, interfaces, and information categories are needed; how access is approved and reviewed; which legal entity will contract; and whether subcontractors or other suppliers will participate. For a supplier, examine traceable company information, relevant tiers, ownership or influence, provenance, resilience, and foundational cyber practices as applicable to the fund’s diligence.
Checkpoint 4: expanded commitment. Before adding systems, information, people, or time, record the evidence that supports the change, the new responsibilities, the acceptance or review point, and the person who approves it. If the response is incomplete, retain the narrower scope or request the missing diligence rather than treating the gap as resolved.
Include questions about security architecture, gaps, risks, policies, procedures, and controls when cybersecurity work is in scope. Include the operational dependencies and control expectations relevant to the financial organization. Keep those questions tied to the proposed work; they do not establish a particular regulatory or security outcome.
A provider does not need to supply every item in one document. The important distinction is between evidence available now, evidence that requires a later diligence step, and a limitation that the provider cannot support. Keep that distinction in the decision record before approving the next level of access.
Write the quote brief as the gate’s decision record
Write the quote brief as the commitment gate’s decision record rather than as a general request for software help. The brief should show what is known, what remains uncertain, what the provider may access, and what the fund will use to decide whether to proceed.
Include these sections:
- Decision to support: State the operating or technology question the work should answer.
- Current evidence: Describe the relevant systems, workflow, technical debt, known constraints, and internal capabilities without sharing unnecessary sensitive information.
- Requested output: Identify the assessment, options, component, modernization activity, integration, or other work under consideration.
- Information boundary: List the information categories, environments, repositories, interfaces, and access levels that may be involved.
- Control context: Identify operational dependencies, control expectations, review participants, and the consequences of an unsuitable change that the provider must understand.
- Responsibilities: Separate provider activities from fund decisions, approvals, access administration, testing, deployment, support, and handoff.
- Evidence request: State which technical explanations, artifacts, responsibility assignments, supplier details, and access responses are required before the commitment expands.
- Engagement boundary: Explain whether the fund is considering bounded analysis, a project, a retainer, augmentation, or a staged path, and identify what remains open.
- Acceptance and exit: State how the output will be reviewed, what ends the phase, and what decision follows.
- Unknowns: List assumptions that must be tested rather than silently embedded in the proposal.
If the architecture, system condition, or information boundary is not sufficiently understood, request a bounded assessment or discovery output instead of forcing a fixed delivery quote. If the plan and acceptance conditions are clear, the brief can support a project proposal. If the plan is clear but capacity is the constraint, state the internal direction and review model needed for added engineers.
Keep the brief suitable for controlled sharing. Use abstractions or redacted examples where possible, and identify what a provider must know before receiving more detailed information. A quote request is ready when its decision, access boundary, evidence request, responsibility record, and next review point are visible.
Choose a bounded provider conversation
A bounded provider conversation should test whether the proposed work, people, controls, and engagement structure fit the decision your fund has already defined. Keep the conversation narrow enough that you can distinguish a relevant response from a generic capability presentation.
Neutech offers custom software development services. Neutech also provides senior software designers and developers to augment product and development teams. Those are separate service facts: one concerns custom development, while the other concerns additional design and development capacity.
Neutech uses Scrum and agile planning for project management. If that approach is relevant to your proposed work, ask how planning, review, documentation, decision ownership, and acceptance would operate within your fund’s processes. A named method does not settle the scope or control boundary; the conversation should connect the method to the assignment you described.
Bring these questions to the discussion:
- What does Neutech understand the decision and business objective to be?
- Which parts of the work are discovery, implementation, support, or added capacity?
- What information and system access would the proposed team require?
- Which people would perform the work, and who would own technical decisions?
- What would be produced at the end of the first bounded phase?
- Which assumptions could change the proposed structure or scope?
- How would your fund review, accept, document, and maintain the resulting work?
- What evidence should be available before any increase in access or commitment?
Use the answers to test fit, not to invite a broader promise. If the provider recommends a different structure from the one you expected, ask which unresolved decision led to that recommendation. If the recommendation depends on information you have not yet shared, identify the smallest safe discovery step that would resolve the dependency.
The services and planning approach described above do not by themselves establish suitability for your specific systems, information boundary, controls, or project outcome. Keep those questions in the evaluation record and require the proposed scope to answer them directly.
Use the decision’s limits to set the next step
The next step should be limited by what you know, what you still need to decide, and what access the work would require. Use advisory or discovery work when the technical direction or system boundary remains uncertain; use augmentation when the plan is clear and capacity is the main gap; use a project structure when deliverables and acceptance conditions are defined.
Before you proceed, confirm that your brief names the business objective, current systems context, information boundary, required expertise, responsibilities, engagement preference, and evaluation criteria. Ask for evidence that fits the proposed access and supplier relationship. NIST’s due-diligence categories provide a practical prompt for examining traceable company information, supply-chain tiers, ownership or influence, provenance, resilience, and foundational cyber practices.
A qualified professional inside your organization should decide whether a proposed engagement fits your fund’s legal, regulatory, investment, cybersecurity, and operational requirements. External technical input can inform that decision, but it does not replace your organization’s own approval and oversight.
If the assignment has a defined objective, prepared constraints, and a clear expectation for external engineering support, the inquiry can begin with a bounded question and an evidence request rather than an open-ended search.
What should a hedge fund clarify before contacting a software consultant?
What does a software development consultant do?
A software development consultant analyzes requirements, identifies strategies, develops or implements software solutions, manages projects, provides technical support, and trains clients on new systems.
When should a hedge fund consider engaging a software development consultant?
A hedge fund should consider engaging a consultant when it needs expert input on unresolved technical decisions, additional engineering capacity for a defined plan, or assistance with implementing a specific software solution.
What are the different engagement models for technology consulting?
Common engagement models include project-based, retainer, and staff augmentation. Each model has distinct contractual mechanics, risk profiles, and appropriate use cases.
How can a hedge fund evaluate a potential software development consultant?
A hedge fund can evaluate a consultant by assessing their technical capability, financial services fit, security and compliance posture, delivery approach, communication skills, team integration, and engagement flexibility.
What information should a hedge fund prepare before requesting a project quote from a consultant?
Before requesting a project quote, a hedge fund should prepare a brief that includes the business objective, current systems context, desired scope, information boundary, required expertise, responsibilities, engagement preference, evaluation criteria, and any questions or unknowns.
What is the importance of defining the control boundary in financial services technology consulting?
Defining the control boundary is crucial to ensure that the engagement aligns with regulatory obligations, cybersecurity exposure, and operational responsibilities, particularly when sensitive information or critical systems are involved.