The decision is larger than selecting a processor
Credit card processing is an operating system of connected roles, software components, controls, and financial records rather than a single feature you can assess in isolation. A processor may help move transaction information and support authorization and settlement, but your organization still has to decide how customers enter payment details, which systems receive transaction events, how responsibilities are divided, and how payment activity is monitored and reconciled.
The right evaluation therefore starts with the payment path. Follow the transaction from the cardholder to the business account, then examine the architecture around that path. This sequence separates three questions that are often blended together:
- What happens in the transaction? Identify the cardholder, business, gateway, processor, acquirer, card network, issuing bank, and settlement process.
- What must your organization control? Examine payment-entry design, website and application security, data handling, access, records, reconciliation, reporting, and operational response.
- What capacity is needed to make the design work? Decide whether your existing team can integrate, test, document, and operate the payment path or whether additional engineering capacity is justified.
Stripe describes the processor as an intermediary that moves transaction information among the business, card network, and issuer, while its processing-flow guidance describes the gateway, processor, acquirer, networks, issuing banks, and settlement stages. Those functional descriptions are more useful than relying on a product label alone. The OCC also distinguishes merchant processing from card issuance: merchant processing concerns the settlement of merchants’ card transactions through card associations, not the bank’s business of issuing cards.
Use this guide to create a bounded decision record. It can help you frame technical and operational questions before a vendor conversation or an engineering staffing decision. It cannot select a processor for your organization or establish situation-specific legal, regulatory, financial, tax, security, or compliance conclusions.
Follow the transaction from cardholder to business account
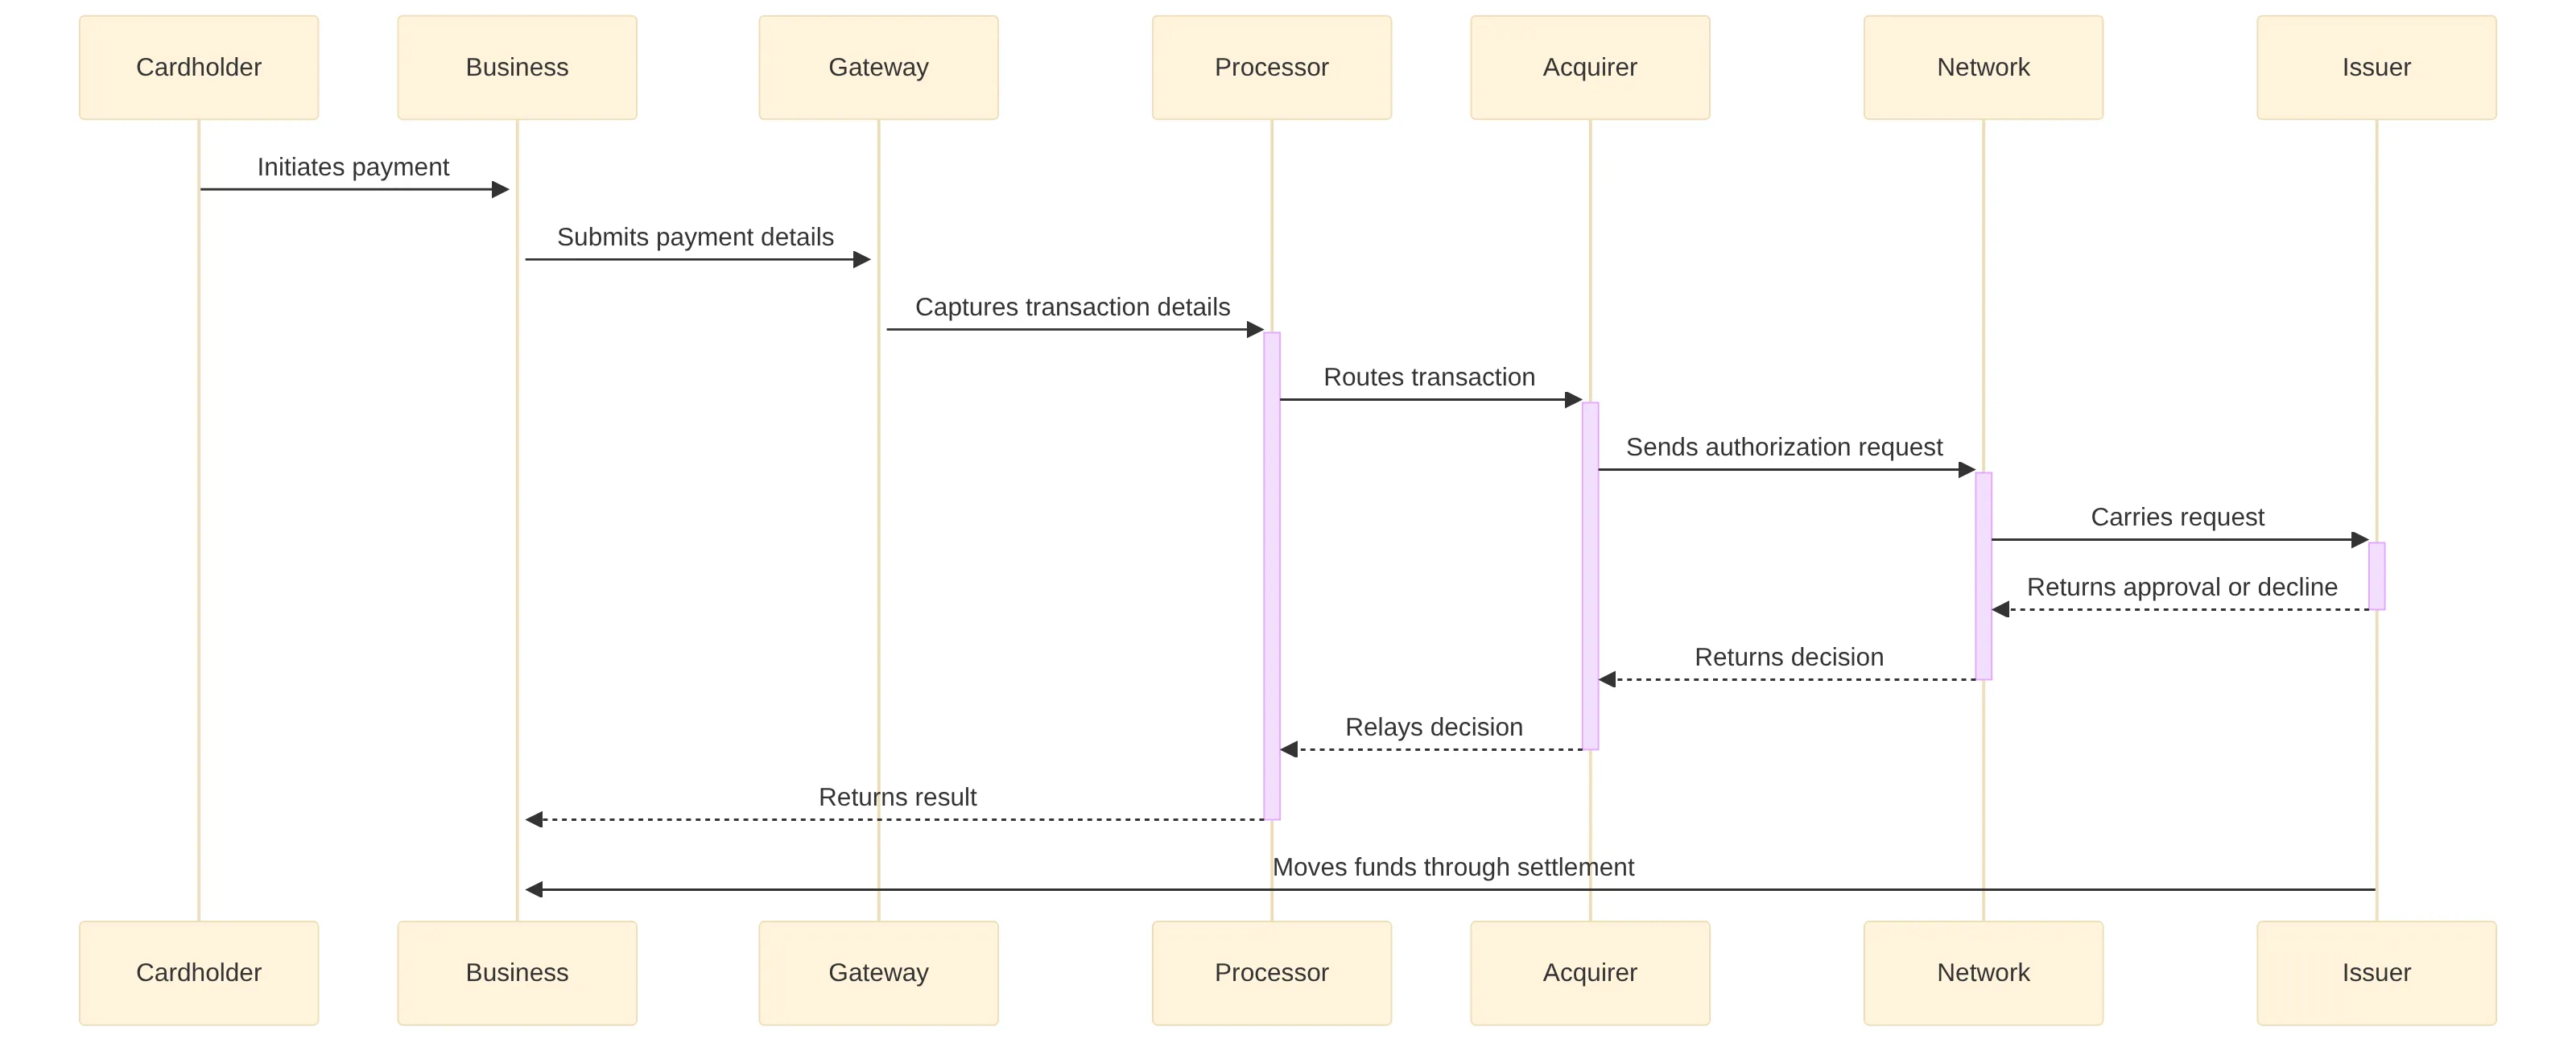
A card transaction begins with the cardholder and ends with settlement toward the business’s account, but several parties handle information and financial movement along the way. Mapping each stage gives you a common vocabulary for architecture, ownership, and troubleshooting.
- The cardholder initiates payment. The cardholder submits payment details through the business’s checkout, application, device, or another payment-entry experience. Your first architecture question is where that information is entered and which application or hosted page receives it.
- The gateway captures the transaction details. The gateway is the payment-entry and connection layer used to send transaction information into payment infrastructure. The exact integration pattern affects what your website or application handles directly.
- The processor and acquirer route the transaction. The processor moves key transaction information among the business, card network, and issuing bank. The merchant acquirer processes card payments for the business and routes them through card networks to the issuer. A payment provider can perform both processor and acquirer functions, so you should map functions rather than assume that separate labels always mean separate organizations.
- The card network carries the request between participants. The network connects the acquiring side with the issuing side during the authorization path. It is one of the functional parties in the transaction, not simply a synonym for the processor.
- The issuing bank approves or declines. The issuing bank evaluates the transaction details and returns an approval or decline through the card network and payment infrastructure. Your application needs a defined way to represent that decision to the customer and to the systems responsible for the order or service.
- The result returns to the business. The processor relays the decision to the business. The customer-facing response and the internal transaction record should be treated as related outputs that your team can trace to the same payment attempt.
- Approved activity moves into settlement. After approval, funds move from the issuing bank toward the business through the payment provider’s settlement process. Settlement is therefore a separate point in the operating path from the initial authorization response.
The distinction between authorization and settlement matters during evaluation. An approved checkout response answers whether the issuer approved the transaction at that stage. It does not, by itself, give you a complete operating view of the funds movement, business records, reporting, or exception handling that follow. Ask your team to draw both paths: the real-time decision path and the later settlement path. Mark every system that creates, receives, transforms, or reconciles a record.
Use the map to assign questions to the right party. Ask the processor or acquirer about the functions it performs, ask your application team how the authorization decision enters business workflows, and ask finance or operations how settlement records will be matched to internal records. Do not treat a single provider label as proof that all responsibilities sit in one place.
Use functional roles when provider labels overlap
Payment-provider labels overlap, so your evaluation should define each functional role before comparing offerings. A processor, acquirer, gateway, network, and issuer can appear in one provider’s commercial description, but those roles answer different questions about the transaction.
- Cardholder: the person whose account supplies the payment and whose card is submitted.
- Business: the organization selling the goods or services and receiving funds through settlement.
- Gateway: the component that captures or passes payment details from the checkout, website, or application into payment infrastructure.
- Processor: the intermediary that moves transaction information among the business, card network, and issuing bank to support authorization and settlement.
- Acquirer: the bank or financial institution that processes card payments for the business and routes them through the card networks toward the issuing bank.
- Card network: the network through which the acquiring and issuing sides communicate during the transaction.
- Issuing bank: the institution that issues the card and returns the approval or decline decision.
The processor and acquirer deserve particular attention because descriptions can make their responsibilities sound interchangeable. Stripe’s explanation distinguishes them as historically separate functions while noting that some payment providers offer both. The OCC’s description of merchant processing likewise centers on banks settling merchants’ card transactions through card associations and separates that activity from card issuance.
Build your provider comparison around explicit questions:
- Which organization performs the gateway function?
- Which organization performs processor and acquirer functions?
- Which party communicates the authorization result to your application?
- Which party produces settlement information for your finance or operations team?
- Which contractual or technical responsibility remains with your organization?
Write the answer in your decision record instead of copying a provider’s category name. That step prevents a commercial label from becoming an accidental assumption about data access, system ownership, support responsibility, or settlement reporting.
Choose the payment-entry architecture deliberately
Payment-entry architecture determines where a customer enters card data and which parts of the payment experience your organization operates. The selected Stripe guidance distinguishes hosted and self-hosted gateways, while PCI e-commerce guidance describes a third-party hosted payment page that sends an acknowledgment back to the merchant application after payment processing.
| Architecture | Where payment details are entered | Security and engineering implication | Decision boundary |
|---|---|---|---|
| Hosted gateway or third-party hosted page | The customer is redirected to the payment provider’s platform or site to complete payment, then returned to the business website or application. | The selected Stripe guidance says this arrangement outsources most security requirements to the provider. Your website and return path still require architectural attention. | Choose this path when redirecting the customer is acceptable and reducing the payment-data handling surface is a stated design objective. |
| Self-hosted gateway | The customer enters payment details on the business website or application, which then sends the data to the gateway. | The business handles and secures payment data, creating greater security obligations for the business. | Choose this path only after your team has defined the controls, ownership, testing, and operating work required by direct handling. |
A hosted design is not a declaration that your organization has no security work. The PCI e-commerce guidance states that weaknesses on the merchant’s website can create a security risk for payment-card data in shared-management implementations, including implementations involving a hosted payment page. Your return URLs, checkout pages, scripts, account controls, and surrounding application can still affect the payment environment.
A self-hosted design may give your team more control over the checkout experience, but control brings responsibilities that must be assigned rather than assumed. Document where payment data enters, where it travels, what is stored, which systems can access it, and how the application handles a failed or interrupted payment. If you cannot name the owner for each control and test, the architecture is not ready for approval.
Make the choice with a short architecture record:
- Draw the customer-facing payment path.
- Mark every system that receives, transmits, displays, or stores payment-related data.
- Identify the provider boundary and your organization’s boundary.
- Record the security obligations created by the selected design.
- Define the acknowledgment, status, and settlement records your application must receive.
The practical action is direct: select the payment-entry pattern only after your team can explain its data boundary and operating responsibilities in plain language.
Treat security scope as an architecture question
Payment security scope follows the way your systems handle payment-card data, so architecture decisions must precede claims about reduced responsibility. PCI DSS is the relevant security standard for payment-card environments, and the PCI Security Standards Council’s quick-reference material points to supporting resources such as self-assessment questionnaires, approved scanning vendors, and qualified security assessors.
Start with the data-flow boundary rather than with a compliance label. Your record should identify:
- Where card data is entered.
- Whether your website or application receives or transmits it.
- Which provider or payment page handles the entry.
- Whether your systems retain payment-related records and in what form.
- Which environments, teams, and vendors can affect the payment path.
- Which assessment or validation activities your organization must address.
The same supplement is supplemental guidance: it does not replace PCI DSS requirements, prescribe every implementation step, or explain how to validate compliance in a tokenized environment. Treat tokenization as an architecture input that requires a scope analysis, not as a conclusion.
The hosted-versus-self-hosted decision changes the questions you must answer. A hosted gateway can move most security requirements to the provider under the selected Stripe guidance, while a self-hosted gateway creates greater obligations because the business handles and secures payment data. Neither statement identifies every obligation for your particular implementation. Your team still needs to examine the website, application, integration points, access paths, and operational ownership.
Use a control-boundary review before implementation:
- Draw the payment-data flow and mark every handoff.
- Assign an owner to each system and integration in the flow.
- Identify which requirements remain with your organization and which are handled by the provider.
- Record the evidence or assessment activity needed for each responsibility.
- Obtain the appropriate situation-specific review before treating the design as compliant.
Keep the conclusion narrow. A payment architecture can influence the scope of work your organization must address, but architecture alone does not validate compliance.
Trace the systems around the payment path
The payment path includes more than the checkout screen, so your technical review should trace the systems that create business meaning around authorization and settlement. The gateway captures transaction details, the payment infrastructure returns an approval or decline, and settlement moves funds toward the business through the provider’s process. Your internal systems must connect those events to the order, account, service, or financial record they represent.
Map the surrounding systems in five layers:
- Customer and channel layer: websites, mobile applications, point-of-sale experiences, or other customer-facing channels that initiate payment.
- Payment-entry layer: the hosted page, gateway, or application component through which transaction details enter the payment path.
- Business-transaction layer: order, subscription, service, account, or entitlement records that explain what the payment is for.
- Settlement and finance layer: records used to match approved activity and settled funds to internal financial records.
- Operations and reporting layer: dashboards, alerts, support workflows, reports, and access controls used to understand payment activity.
For each layer, write the event, owner, source of truth, and handoff. For example, the authorization response may update an order status, while later settlement information may need to be matched to a separate internal record. Do not assume that the system receiving the first response is also the system that can explain the final financial position.
Your integration assessment should answer practical questions:
- Which event starts the internal workflow?
- Which record connects the payment attempt to the customer’s order or account?
- How does the business distinguish an approved authorization from a completed settlement?
- Where can operations see payment status and investigate a mismatch?
- Which reports are needed by engineering, finance, customer support, and leadership?
- Which system owns retries, status updates, and manual review when records do not align?
These are design questions, not assumptions about a particular provider’s features. Ask the provider to explain the data and events it makes available, then ask your engineering team to show how those inputs will be represented internally. A useful integration plan names the source, destination, owner, and expected state for each material handoff.
Treat reconciliation and reporting as first-class design work. If the team evaluates only whether a customer sees an approval, it has not yet shown how the organization will understand settlement, investigate discrepancies, or produce an operational view of payment activity.
Test operational fit beyond successful authorization
Operational fit includes the work that follows a successful authorization, so your evaluation should test usability, scale, support, security, contract terms, reconciliation, and reporting together. The U.S. Chamber guidance identifies ease of use, scalability across sales channels, payment methods and transaction volumes, payment-system features, support and security reputation, and contract terms such as termination fees as evaluation criteria.
Turn those criteria into questions your team can answer:
- Usability: Can the teams responsible for checkout, operations, finance, and support understand the relevant status and records without creating a separate manual interpretation for every transaction?
- Channels and methods: Can the proposed design accommodate the sales channels and payment methods that your organization has defined for the initiative?
- Volume and growth: What transaction-volume assumptions must the provider and your internal systems support, and what changes when those assumptions no longer hold?
- Features: Which required payment-system features are available, and which would require custom work in your application?
- Support: How are technical questions, transaction issues, and operational incidents assigned and escalated across the provider and your organization?
- Security responsibility: Which controls remain with your team under the selected architecture, and where is supporting evidence maintained?
- Reconciliation: Which records will your finance or operations team compare, and how will a mismatch become an owned work item?
- Reporting: Which reports must exist for engineering, finance, customer support, and leadership, and which party supplies the underlying data?
- Contract terms: What terms govern the engagement, including termination fees and other conditions that affect the organization’s ability to change direction?
An approved payment shows only the happy path. For reliability and recovery, assess how an operational incident or mismatched record is handled, and record the responsible party, supporting evidence, acceptance condition, and recovery path. Ask for scenarios that match your decision record: a payment entered through the selected channel, an authorization response returned to the application, settlement information reaching the financial workflow, a report generated for the appropriate audience, and an ownership path for a record that does not match.
Do not convert a provider’s feature list into an assurance about your result. Record the specific capability, the system boundary, the responsible party, the evidence you need, and the acceptance condition. Then test the path with the people who will operate it, not only the engineers who build the integration.
Make vendor diligence evidence-based
Vendor diligence should begin with the provider’s actual role and data access rather than with a broad reputation or category label. The selected financial-services diligence guidance recommends defining the vendor’s services and responsibilities and documenting the types of data the vendor will access, process, or store.
Create a diligence brief with four parts:
- Service boundary. Describe the payment functions the vendor will perform, the functions your organization will retain, and the systems connected to the service.
- Data boundary. List the data the vendor may access, process, or store. Distinguish payment-related data from the business, customer, order, and reporting records that surround it.
- Control evidence. Request the security policies and procedures, certifications and attestations, audit reports, incident history, and ownership information identified in the diligence guidance.
- Operating responsibility. Assign responsibility for support, incident communication, access management, integration changes, reporting, and settlement-related investigation.
The request is not complete merely because documents have been collected. Link each document or response to a question in your decision record. If you are assessing the provider’s security controls, identify the control, the evidence that addresses it, the period or scope covered by that evidence, and the party responsible for interpreting it. If you are assessing operational support, identify the workflow, the handoff, and the acceptance condition.
PCI DSS resources can help you identify relevant assessment paths, including self-assessment questionnaires, approved scanning vendors, and qualified security assessors. Those resources do not turn a vendor document into a conclusion about your own environment. Keep the provider’s responsibilities and your organization’s responsibilities separate in the record.
Use a simple status for each diligence question: answered, evidence received, follow-up required, or unresolved. An unresolved item should have an owner and a decision date set by your internal process. Do not approve the architecture because the diligence folder is full; approve it only when the material responsibilities, data access, controls, and operating questions have an explicit disposition.
Separate processor capability from engineering capacity
Processor capability and engineering capacity are separate decisions: the provider supplies defined payment functions, while your organization still has to make the selected architecture work inside its applications, controls, records, and operating routines. A provider’s ability to authorize or settle transactions does not tell you whether your team has enough capacity to integrate the service, connect surrounding systems, document responsibilities, test the flow, or maintain it.
Assess engineering capacity against the decision record rather than against a generic headcount target. Ask whether your team has an accountable owner and enough time for:
- Mapping the payment and settlement paths.
- Implementing the selected gateway or payment-entry architecture.
- Connecting checkout, business-transaction, finance, reporting, and support systems.
- Defining access, data handling, and control ownership.
- Testing authorization, settlement, reporting, and reconciliation paths.
- Resolving integration issues with legacy technology.
- Maintaining the integration as the organization’s payment requirements change.
Legacy-technology integration is a concern for B2B operations.. Do not describe that situation as a processor deficiency without examining the integration boundary. The constraint may be the work required to connect the provider to the organization’s existing environment.
At Neutech, we provide senior software designers and developers to augment product and development teams. Our senior engineers ship custom software development solutions. Those are defined services; they do not make Neutech a credit card processor or independently provide payment-processing infrastructure.
Additional engineering capacity may be relevant when the organization has selected or narrowed an architecture but lacks enough internal time to complete the integration and operating work. It may be less relevant when the payment path is not defined, responsibilities are unresolved, or the organization has not decided which systems must connect. In that situation, resolve the decision boundary first, then size the engineering work against named deliverables.
Use a clear handoff between the two decisions. Ask the provider what payment capability and data interface it supplies. Ask your engineering team what must be built, tested, monitored, documented, and supported around that capability. Request outside capacity only for the gap you can describe.
Use a bounded decision record before implementation
A payment-processing decision record should capture the chosen boundary, the unresolved questions, and the work required before implementation begins. Use the record as an internal review artifact and as the agenda for provider and engineering conversations.
Include these fields:
- Decision statement: What payment capability or architecture is being evaluated, and what decision must be made?
- Transaction map: Who performs the cardholder, business, gateway, processor, acquirer, network, and issuer functions? Where does settlement fit?
- Payment-entry design: Is the customer redirected to a hosted payment page, or does the business application collect payment details? What responsibilities follow from that choice?
- Data-flow boundary: Which systems receive, transmit, display, or store payment-related data? Where are the provider and organization boundaries?
- Integration map: Which checkout, order, account, finance, reporting, support, and legacy systems connect to the payment path?
- Control and assessment questions: Which PCI DSS resources, assessments, evidence, and professional reviews apply to the organization’s situation?
- Operational acceptance: How will the team represent authorization, settlement, reporting, reconciliation, support ownership, and unresolved exceptions?
- Vendor diligence: What services, responsibilities, data access, security evidence, incident history, ownership information, and contract terms require disposition?
- Engineering ownership: Which work belongs to the internal team, which work belongs to the provider, and where is additional capacity required?
- Open decisions: Which items remain unresolved, who owns each item, and what evidence or action closes it?
Keep each field specific enough to support a decision. For example, “security review required” is weaker than “identify the systems that receive payment data, assign their owners, and define the assessment activity for the selected architecture.” “Integration needed” is weaker than naming the checkout, order, settlement, reporting, and support handoffs.
The record should also distinguish facts, assumptions, questions, and decisions. A provider statement belongs in the evidence or diligence area until your team has determined how it affects the organization’s environment. A proposed design belongs in the decision area only after the affected systems and responsibilities are named.
Use the completed record to decide whether to proceed, obtain more information, change the architecture, or define an engineering work package. Keep the next decision bounded; do not approve an entire payment program because one transaction path has been demonstrated.
Know what this evaluation cannot decide
A credit card processing evaluation can organize your technical and operational questions, but it cannot by itself produce every decision your organization may need. Keep the boundaries explicit so a useful architecture guide is not mistaken for an approval or assurance.
This evaluation cannot decide:
- Whether a particular processing arrangement satisfies the legal or regulatory requirements that apply to your organization, product, customers, or jurisdictions.
- Whether a surcharge, pricing practice, tax treatment, or financial arrangement is permitted or appropriate for your situation.
- Whether a provider has a certification, audit result, security control, or contractual commitment that has not been examined in its relevant scope and period.
The PCI SSC tokenization guidance expressly treats its material as supplemental and does not replace PCI DSS requirements or validate compliance in a tokenized environment. - Whether a hosted payment page removes all security responsibility from your organization. Weaknesses in a merchant website can create a security risk for payment-card data in shared-management e-commerce implementations.
- Whether a processor will deliver a specific fee, processing time, approval rate, uptime result, profitability result, or business outcome. The selected commercial guidance supports evaluation criteria, not a promise of a particular result.
- Whether your internal team or an outside engineering team can deliver the integration until the systems, controls, acceptance conditions, and available capacity have been defined.
Use the boundary to decide what must be escalated. A technical team can map data flows and build tests. Operations can define reporting and support workflows. Finance can define settlement and reconciliation requirements. The appropriate internal authority or qualified adviser must address questions that depend on your organization’s facts and obligations.
The practical result is a better-scoped next step, not a universal answer. If a question cannot be answered from the transaction map, architecture record, diligence evidence, or assigned professional review, keep it open and assign an owner rather than turning an assumption into a selection criterion.
Decide whether additional engineering capacity is justified
Additional engineering capacity is justified when the payment decision has produced a defined body of integration, control, reconciliation, reporting, or maintenance work that exceeds the team’s available capacity. The question is not whether outside engineers can replace a processor; they cannot. The question is whether the organization can complete and operate the surrounding software work with the people, time, and technical ownership already available.
Use the decision record to sort the situation into one of three paths.
Keep the work within the existing team when:
- One accountable owner can coordinate the payment path and surrounding systems.
- The selected architecture and data boundary are documented.
- Internal engineers have time for implementation, testing, documentation, and operational handoff.
- Finance, support, security, and engineering agree on the acceptance conditions.
- Legacy integration work is understood and fits the available technical capacity.
The direct action is to assign the work package, owner, milestones, and acceptance tests internally.
Define additional capacity when:
- The architecture is sufficiently bounded, but integration crosses several systems or ownership boundaries.
- The team must connect a payment entry point to order, account, settlement, reconciliation, reporting, or support workflows.
- Legacy technology creates integration work that the current team cannot absorb without displacing committed delivery.
- The organization needs implementation and documentation capacity at the same time as it maintains existing payment operations.
- The work has a clear start point, deliverable set, technical owner, and review path.
The direct action is to turn those gaps into a scoped engineering work package rather than requesting generic extra capacity.
Resolve the decision before adding capacity when:
- The organization has not chosen the payment-entry architecture.
- The provider’s functional role, data boundary, or settlement path is unclear.
- Control responsibilities and assessment questions remain undefined.
- The requested team would be expected to discover the business decision, select a provider, and implement the result without an accountable internal owner.
The direct action is to finish the decision record and diligence questions before sizing the build.
At Neutech, we provide senior software designers and developers to augment product and development teams, and our senior engineers ship custom software development solutions. If the defined gap concerns implementation or integration work, describe the systems, responsibilities, acceptance conditions, and available internal capacity before asking for outside support.
Request a project quote with the decision record
A sound payment-processing decision leaves you with more than a processor name: it gives you a transaction map, a defined payment-entry architecture, a documented security boundary, an integration and reconciliation plan, an operational test set, a vendor diligence record, and an explicit engineering-capacity decision.
Use that record to separate what the payment provider supplies from what your organization must build, control, validate, and operate. If the remaining work is defined and your internal team cannot absorb it, describe the payment flow, connected systems, control responsibilities, acceptance conditions, and engineering gap in the next project conversation.
This article provides general educational guidance. A qualified professional must determine individual legal, regulatory, financial, tax, security, or compliance suitability for your organization’s circumstances.